- Home
Cyber Security Agency of Montenegro Cyber Balkans II: Orahovac Presents Progress and P...
Cyber Balkans II: Orahovac Presents Progress and Priorities for Strengthening Cyber Resilience

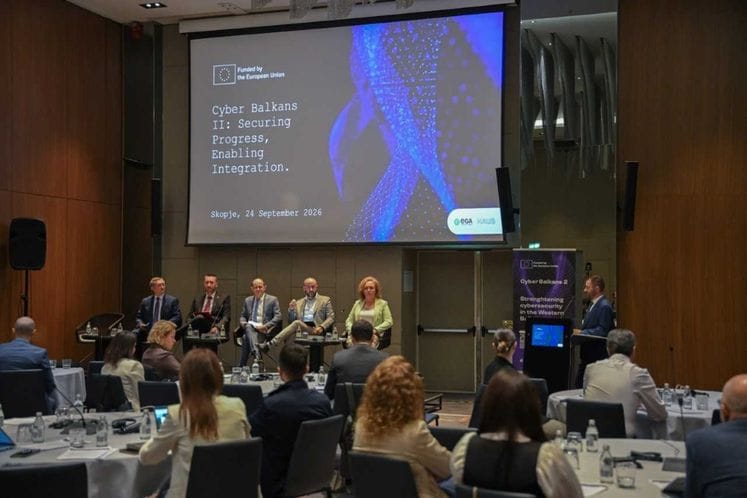
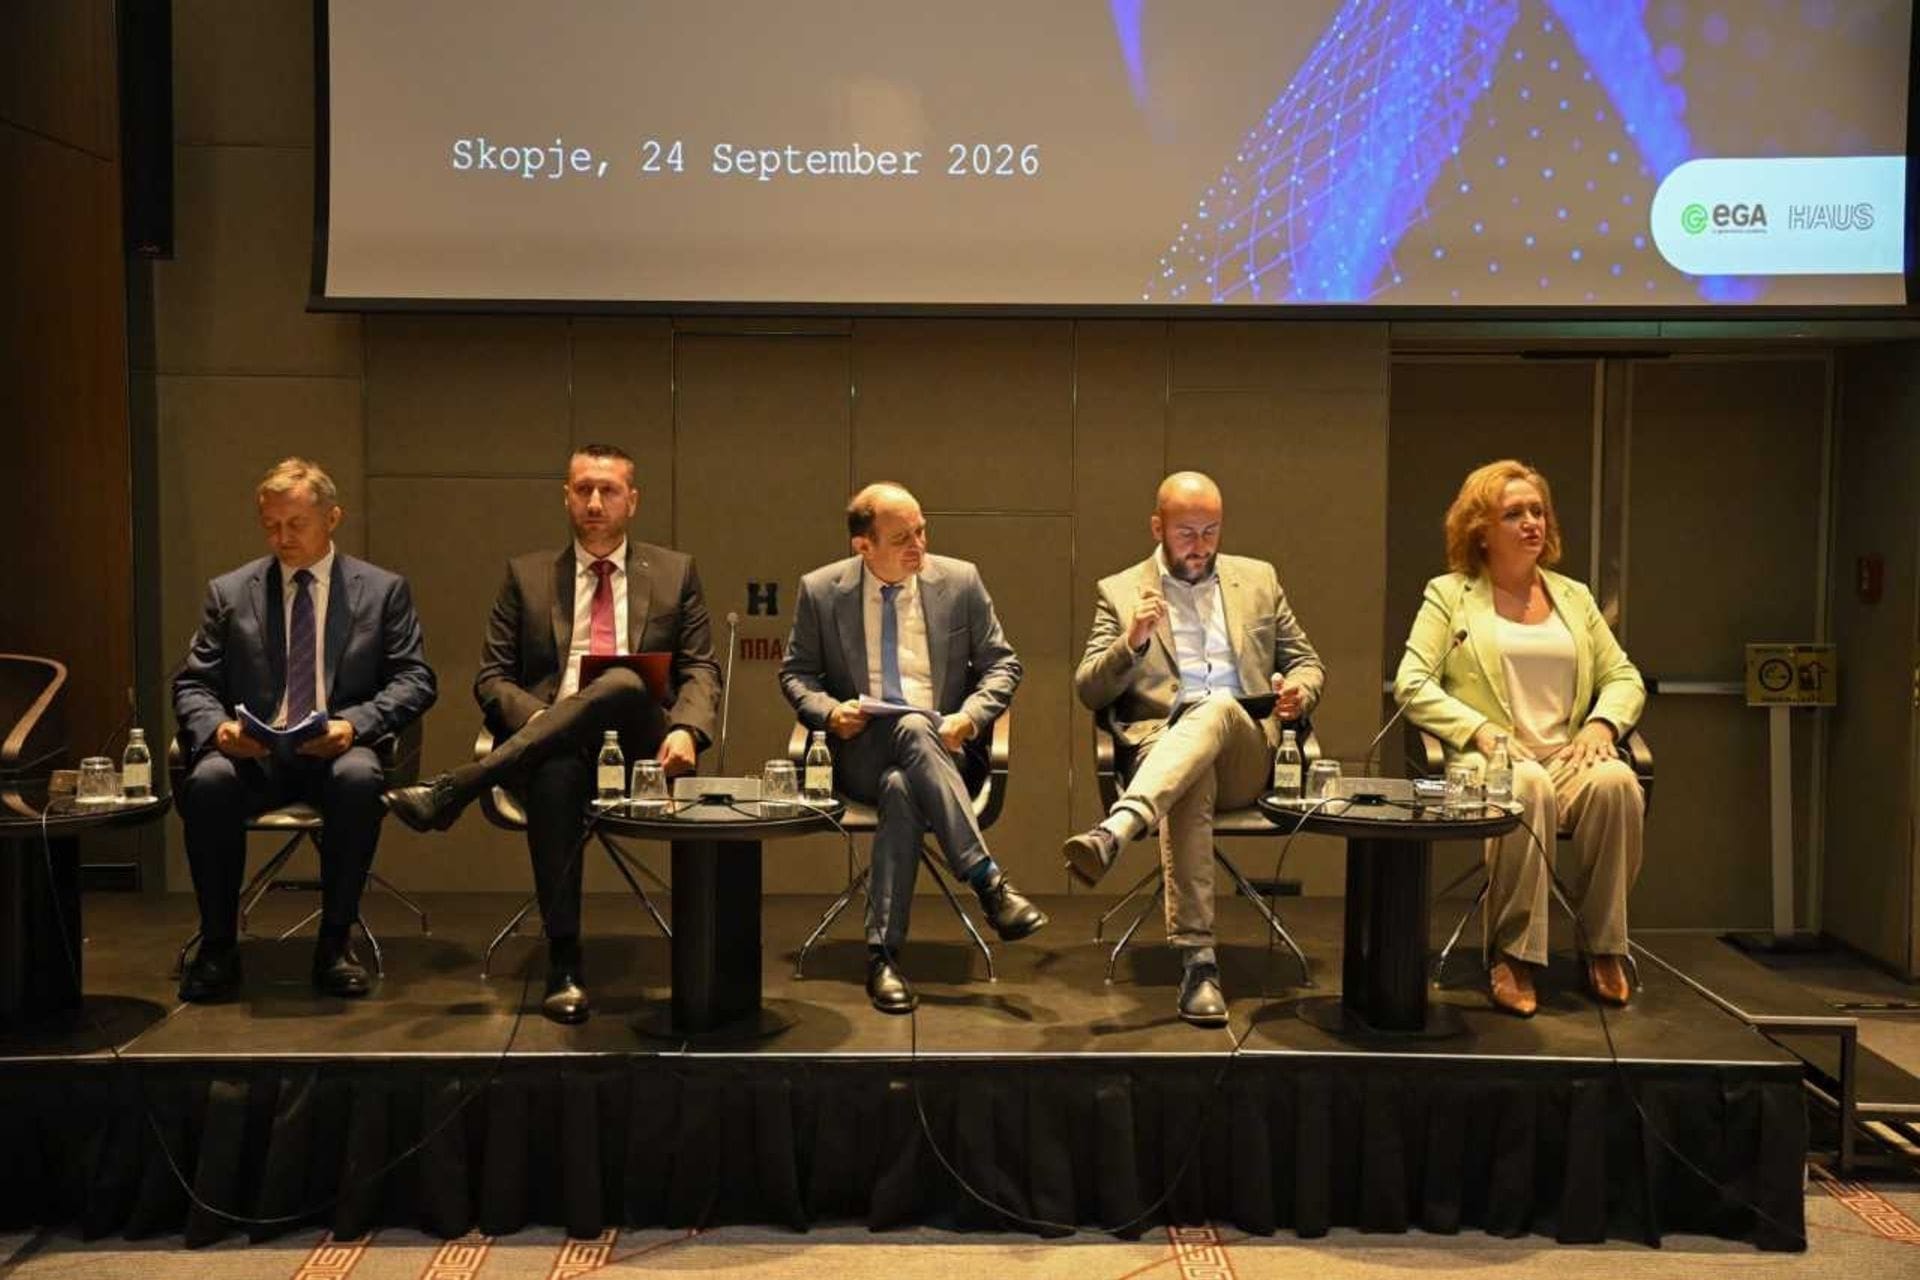
The Cyber Balkans II - Setting the Course for Cyber Resilient Region conference was held in Skopje, focusing on strengthening the Western Balkans' cyber resilience and continuing support for countries in the region to align with the EU acquis and international standards.
The Cyber Balkans II project is funded by the European Union and implemented by the e-Governance Academy (eGA) of Estonia and the Finnish Institute of Public Management (HAUS), in cooperation with the Centre for International Legal Cooperation (CILC) of the Netherlands and the National Cyber and Information Security Agency (NÚKIB) of the Czech Republic, with expert support from the national CERTs of Latvia and Slovenia.
During a panel discussion on key achievements, Orahovac highlighted that over the past three years, Montenegro has made significant progress in strengthening its legal and institutional cybersecurity framework. In particular, he pointed to the adoption of the new Law on Information Security, which further aligns the national system with the requirements of the NIS2 Directive, as well as the establishment of a clearer framework for key and important entities and their responsibilities in the area of information security.
As an important part of institutional development, he also highlighted the adoption of the Cybersecurity Strategy and the National Plan for Response to Cyber Threats, Incidents and Crises, as well as the establishment of the Cybersecurity Agency of Montenegro.
Discussing the advancement of operational capacities, Orahovac emphasized the significance of establishing the Government Security Operations Centre (GSOC) and both the Government and National CIRTs. He noted that both CIRTs have earned TF-CSIRT accreditation, marking a key endorsement of their expertise and maturity.
“Montenegro has built a much stronger and more organised cybersecurity system than we had before,” Orahovac said, stressing that the next step is to ensure that the existing system is effectively implemented in practice.
In this context, he also presented the launch of the first supervisory activities on the implementation of information security measures among key and important entities. As he noted, the aim of supervision is not only to assess compliance with the law, but also to identify the challenges organisations face, improve their security, and build effective cooperation with supervised entities.
Among the priorities for the coming period, Orahovac highlighted strengthening cybersecurity knowledge and awareness, developing human capacities, improving cooperation between institutions, and attracting and retaining cybersecurity professionals in the public sector.
“For Montenegro, we can describe our priorities for the next three years very simply: strong institutions, skilled people and good cooperation,” Orahovac said.
The Skopje conference marked the start of a new phase in the Cyber Balkans project, which aims to build a more cyber-resilient Western Balkans by promoting the exchange of experience, providing expert support, and strengthening regional cooperation.